RALEIGH – A state audit released Friday says auditors reviewed selected cybersecurity controls at the North Carolina Secretary of State, but the public report withholds the findings and recommendations to protect sensitive state interests and data.
The Office of the State Auditor said the review examined whether selected control activities complied with the Statewide Information Security Manual. The report does not identify the systems tested, describe the issues found or state how many findings or recommendations were made.
The two-page public report also does not allege a breach, say that information was compromised or characterize the severity of any undisclosed issue. Those limits matter because the existence of confidential findings does not establish facts the public report does not provide.
Auditors reported spending 2,304 hours on the work at an approximate cost of $355,538. The report is addressed to Gov. Josh Stein, Senate leader Phil Berger, House Speaker Destin Hall, members of the General Assembly and Secretary of State Elaine Marshall.
The North Carolina Department of Information Technology describes the Statewide Information Security Manual as the baseline security standard for state agencies. The department says the manual uses the National Institute of Standards and Technology’s Special Publication 800-53 Revision 5 and organizes requirements across 18 control families.
State law separately gives the State chief information officer authority over security standards and risk assessments. It also says detailed reports identifying risk and security issues are confidential, while preserving the State Auditor’s authority to assess state information-technology security practices.
The audit provides public confirmation that the statewide elected office’s cybersecurity controls received review, along with the audit’s scope, time and cost. It does not provide enough detail to evaluate the nature of the findings or the agency’s response. Any later public response, remediation record or follow-up audit would be a separate development requiring its own verification.
Sources
- North Carolina Office of the State Auditor: Secretary of State cybersecurity controls audit
- North Carolina Department of Information Technology: statewide information security policies
- North Carolina General Statutes § 143B-1377: security standards and risk assessments
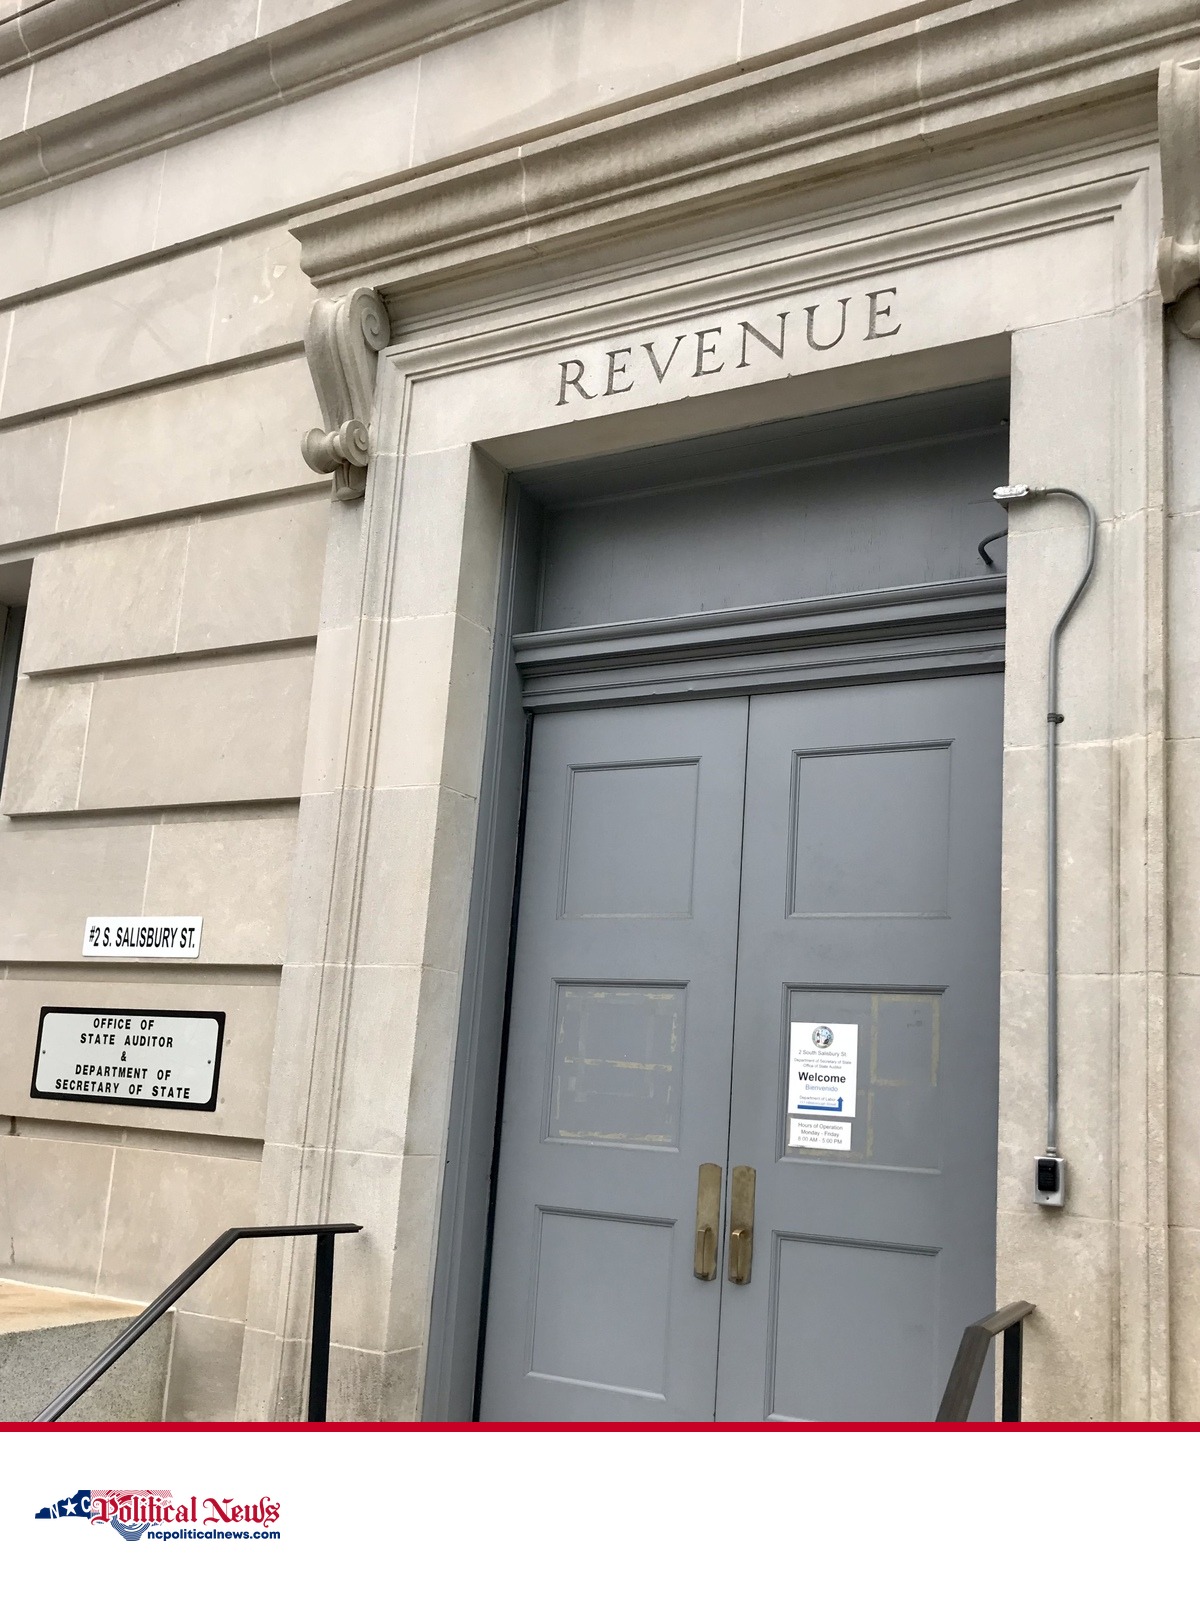
Photo Credit: Indy beetle, via Wikimedia Commons. CC0 1.0 public-domain dedication. The April 16, 2023 photograph shows the public entrance to Raleigh’s Old Revenue Building, which houses offices of the North Carolina Secretary of State and State Auditor. Cropped and resized. NCPN logo is a separate brand mark.
Editor’s Note: This article was drafted with the assistance of artificial intelligence and was reviewed and fact-checked by a member of the NC Political News editorial team before publication.